Protect Your Accounts From Phishing, Smishing and Vishing Scams
Fraudsters don't always need an elaborate scheme to steal your money. Phishing, smishing and vishing scams—which begin with a fake message that often claims to come from a trusted organization like a financial services firm or government agency—are among the most common and effective tools for fraudsters. Knowing how to recognize and protect yourself against “-ishing” scams can help you safeguard both your identity and your assets.
How to Recognize “-ishing” Attempts
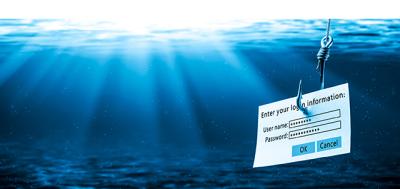
A type of cyber-enabled fraud, “-ishing” scams often start with an email, text or encrypted message that falsely claims to be from a financial institution, electronic payment service, mail delivery company, electronic signature platform or another familiar organization or service. Sometimes, the message appears to be from a government or regulatory agency. The message might come via email (phishing scams), text or encrypted message (smishing scams), or a phone call or voicemail (vishing scams).
To seem genuine, these pitches often use:
- the names of real people or organizations;
- legitimate-looking addresses, such as support@[name of your financial institution].com;
- authentic-looking logos and graphics;
- links to pages of a seemingly credible website; and
- official-looking fine print and references to laws.
Most “-ishing” campaigns attempt to lure you into sharing sensitive personal information by requesting that you reply to the sender or click on a link that mimics a legitimate website.
Phishing or smishing scams might also encourage you to click on a link or download files that will then secretly install malicious software on your device. This malware can take many forms. Some malware programs log your keystrokes, thus allowing scammers to learn your usernames and passwords, giving them access to your online accounts. Others, referred to as ransomware, encrypt or otherwise block access to your files, after which the bad actor demands payment (often in crypto assets) to restore access to your data and perhaps your device itself.
Scammers might also use electronic signature platforms—like DocuSign—to gain access to sensitive personal and financial data and facilitate fraudulent payment requests. In these schemes, bad actors send emails containing fake documents and attachments from authentic electronic signature platforms and imitate legitimate signature requests. Materials might encourage you to open a digital wallet on a fraudulent crypto asset trading platform or could look like a contract or legal document. Other examples include phony offers of employment opportunities, debt relief, government assistance or technical support services.
Messages in “-ishing” scams often apply urgency to incite you to act, such as claiming that your account has been or will be shut down unless you click the link, or that you need to verify your identity (and provide sensitive information) due to fraudulent or illegal activity using your data.
In targeted attacks, sometimes known as “spear phishing,” scammers send messages that appear to be from an individual you know. These “friend” or “colleague” emails seem plausible—for instance, an email that looks like it’s from your company’s human resources department asking for updated personal information, or a video that appears to be recommended by someone you know.
Protect Yourself From “-ishing” Attempts
Always stay vigilant online and be skeptical of unexpected messages, as cybercrime changes at a rapid pace. For example, misspelled company names and jumbled website URLs were a clear tipoff to phishing ploys in the past. But scammers have evolved their tactics, and now seemingly legitimate links can hijack users to a fraudulent site through code buried behind the message. These scams now also sometimes incorporate generative artificial intelligence (GenAI) elements, making them difficult to distinguish from authentic communications.
This makes it especially critical that you don't reply to or click on a link in an unsolicited message—via email, text, encrypted message or any other electronic platform—even if it seems to come from someone you know or an institution with which you do business.
Taking these additional steps can also help you protect your information:
- Verify the claim or request by independently logging on to the company’s main website or calling using a telephone number obtained from a separate source. Rather than clicking on an included link or scanning a sent QR code, type the URL found on a legitimate account statement directly into your browser, check the account using the associated app on your mobile device, or call the phone number found on the back of your credit card or on the entity’s official website to verify asks before taking any action.
- Check whether an email address or text might be mimicking a legitimate sender. For instance, does the visible sender name match the underlying email address? Does the message come from a public email server, such as Gmail, but say that it’s from a business or government agency? Does the text come from an email address or an unfamiliar number? If you suspect a scam, block the sender, and report the message as junk or spam.
- Use only secure networks to access your financial accounts, consider enabling multi-factor authentication (MFA), if available, and be sure to create strong passwords for your accounts and any financial apps you use.
- Use FINRA BrokerCheck to ensure the firm and financial professional are properly registered and verify the contact information you receive before you open an account or give anyone access to your money. This can help you avoid broker imposter scams.
- Regularly review your account statements and activity for unrecognized transactions, and immediately report any suspicious activity to your financial institution. Check your credit report annually as well, looking for accounts you didn’t open and any unexplained activity.
If you have information about potentially fraudulent, illegal or unethical activity, contact your local law enforcement and the FBI (Field Office or Electronic Tip Form), and submit a regulatory tip to FINRA. You can also report fraud to the Federal Trade Commission (FTC). If you think you’ve been the victim of any cyber-enabled scam, file a report with the FBI’s Internet Crime Complaint Center. If you believe your identity has been stolen, the FTC’s Identity Theft resource can help.